
A single leaked customer file, a ransomware-infected workstation, or an agent falling for a phishing email can end a long client relationship and trigger regulatory fines. For BPOs operating in the Philippines, where global clients expect strict protections and local regulators enforce data privacy, security is not an add-on. It must be embedded into every policy, process, and piece of technology.
This article explains pragmatic, specific approaches to BPO security Philippines teams can implement now. You will find the compliance landscape that matters for Philippine providers, practical controls that address the most common threats, ways to demonstrate security to clients and auditors, and operational tips that preserve productivity while reducing risk.
Why BPO security Philippines matters for clients and regulators Clients contract Philippine BPOs for cost efficiency and reliable operations, but they also outsource sensitive data and business-critical services. Payment card data, healthcare records, financial account information, and proprietary business processes all pass through BPO environments. A breach harms customers, damages client brands, and usually triggers legal obligations.
Two forces make security urgent. First, regulators require demonstrable protections for personal and financial data. The National Privacy Commission enforces the Data Privacy Act, which governs how personal data is collected, processed, and transferred. Financial services clients bring their own regulator expectations, such as guidelines from the Bangko Sentral ng Pilipinas. Second, global clients often demand international standards such as ISO 27001, PCI DSS, SOC 2, or HIPAA compliance. Philippine BPOs must meet both local and client-driven controls, and that creates a layered compliance obligation.
Common threat scenarios for Philippine BPOs and realistic consequences Understanding threat scenarios makes it easier to prioritize controls. Several recurring incidents cause most damage:
- Phishing attacks that compromise agent credentials, allowing access to CRM systems and customer accounts.
- Ransomware that spreads from a single workstation to shared file servers and backup systems, interrupting service.
- Insider risk, whether intentional or accidental, where employees exfiltrate or expose customer data.
- Misconfigured cloud storage buckets or APIs that leak datasets to the internet.
- Physical breaches or theft during power outages or extreme weather events that interrupt security monitoring.
Consequences include client contract termination, penalty clauses, notification obligations under the Data Privacy Act, loss of future deals, and the direct costs of incident response and remediation. Mitigating these risks requires targeted, practical measures that align with how BPOs operate day to day.
Key compliance frameworks and Philippine regulators to know BPO security Philippines teams should map their obligations across three layers: local law, client contractual requirements, and international standards.
The National Privacy Commission enforces the Data Privacy Act of 2012. That law requires lawful processing bases, data subject rights mechanisms, breach notification, and reasonable organizational and technical safeguards. For financial services engagements, the Bangko Sentral ng Pilipinas issues circulars and guidelines that affect cybersecurity and third-party risk management. Healthcare clients will expect HIPAA-equivalent safeguards even if HIPAA itself does not directly apply, and payment processing brings PCI DSS requirements.
International certifications carry practical benefits beyond audit checkboxes. ISO 27001 provides a management framework that auditors and clients recognize. SOC 2 reports are commonly requested by U.S. clients seeking assurance about controls over security, availability, and confidentiality. PCI DSS applies when cardholder data flows into your environment. Match your controls to the standards your clients require, and maintain evidence so audits are straightforward.
Physical security and site design that reduce human risk A secure physical environment stops many common incidents before they start. For BPOs in the Philippines, physical controls must balance high agent density, shift operations, and, in some locations, shared office buildings or malls.
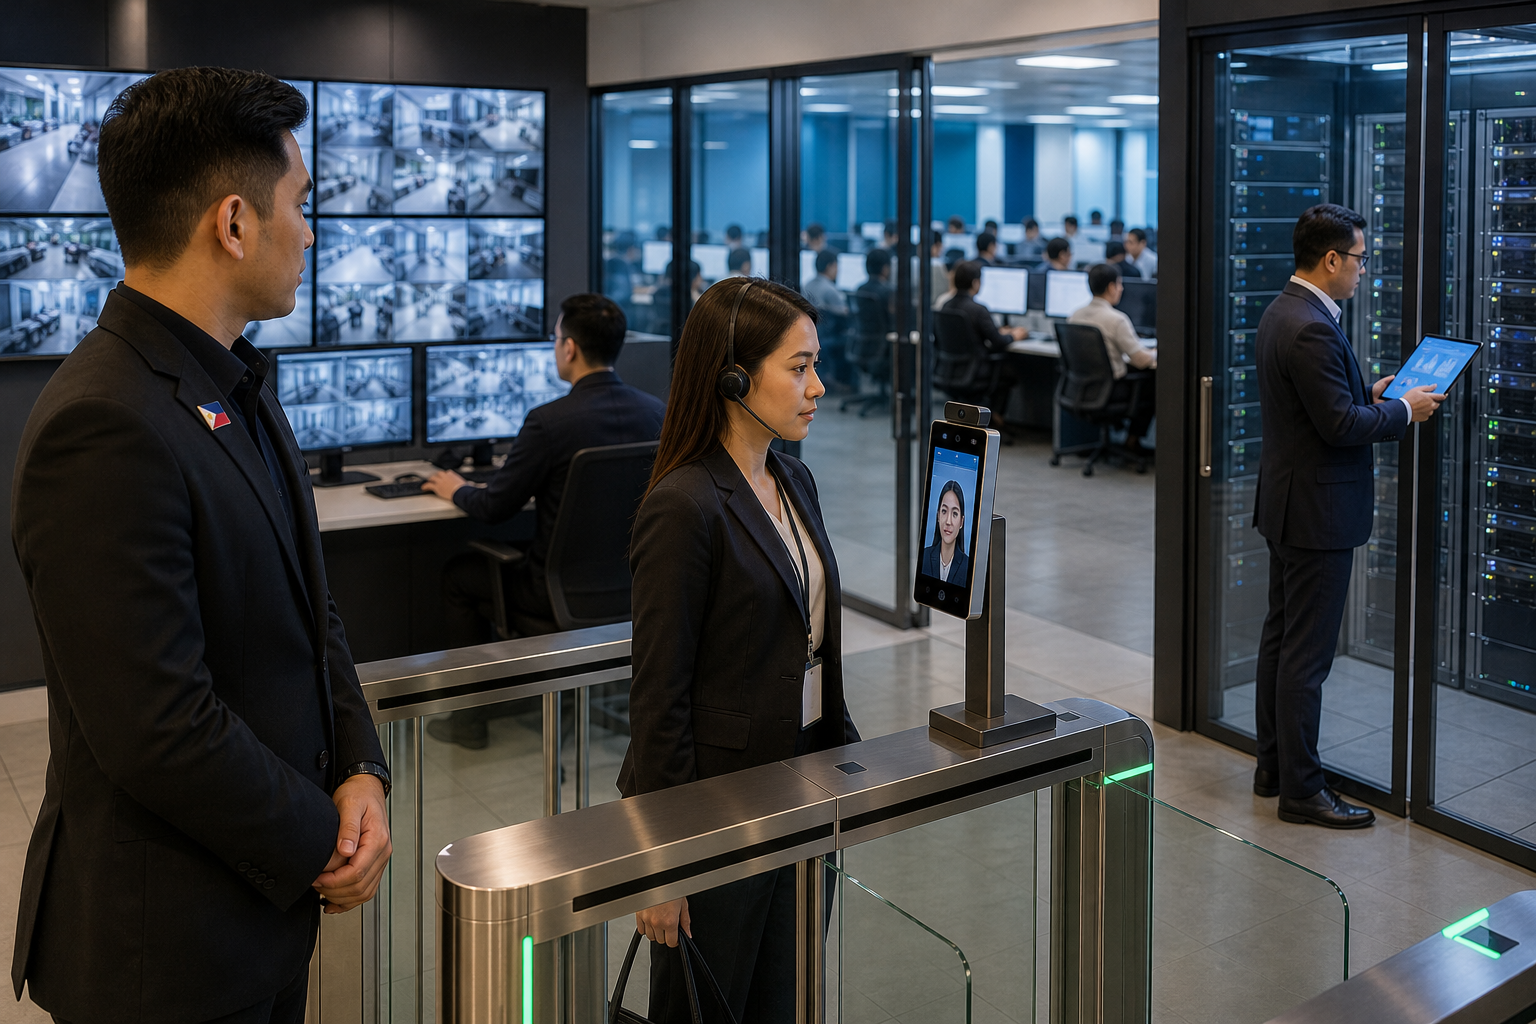
Start with controlled entry points. Use manned reception with visitor logs, electronic access cards tied to HR systems, and turnstiles or controlled doors for floor access. CCTV should cover all entry points and critical areas, and footage retention must align with privacy rules and client contracts. Maintain separate secure rooms for servers and network equipment, with access limited to authorized IT staff.
Design workspaces to reduce data exposure. Where agents handle sensitive data, use privacy screens, seating layouts that reduce shoulder-surfing, and quiet zones for shared screens. For client rooms or voice centers that require heightened privacy, enforce clean desk policies and provide secure lockers for personal items.
Power stability and environmental resilience are practical concerns. Install uninterruptible power supplies and tested generator failovers for critical equipment. Protect physical sites against flooding or typhoon damage using raised server racks and location-aware evacuation plans. Regularly exercise recovery procedures during off-peak hours so staff know their roles when weather or infrastructure events occur.
Identity, access, and employee lifecycle controls Human error and compromised credentials cause a large share of incidents. Effective identity and access management reduces exposure without making daily work painful.
Enforce least privilege across systems, granting employees only the access they need for their job. Use role-based access controls mapped to documented job functions. For privileged accounts, implement privileged access management with session recording and approval workflows.
Multi-factor authentication should apply to all remote access, administrative accounts, and any system that stores or processes sensitive data. Where possible, replace passwords with modern authentication methods, such as hardware tokens or FIDO2 keys.
Control the employee lifecycle tightly. Conduct background checks that comply with local law before onboarding staff in sensitive roles. Integrate HR and IT so that when someone changes role or leaves, access is adjusted or revoked immediately. Maintain audit trails for access changes and periodic certifications where managers verify that only current staff retain sensitive privileges.
Network, endpoint and cloud controls that stop attackers at scale BPO operations rely on complex networks, often combining on-premises infrastructure and cloud services. Architect networks to limit lateral movement and contain incidents.
Segment the network so that agent desktops cannot directly reach server segments where sensitive data is stored. Use microsegmentation where possible to limit east-west traffic. Control remote access with hardened jump servers and gateways, rather than allowing direct VPN access to production systems.
Endpoint protection must include managed detection and response capabilities. Standard antivirus alone is not sufficient. Deploy endpoint detection, centralized logging, and behavioral analytics that can detect unusual patterns such as mass file encryption or credential abuse. Keep endpoint configurations standardized and patched on a regular cadence that balances risk and operational disruption.
For cloud environments, apply the same security rigor as on-premises assets. Use identity-based access controls, enforce encryption at rest and in transit, and monitor cloud storage for misconfigurations. Automate discovery of publicly exposed services and run regular API security checks.
Create strong backup and recovery workflows. Backups should be isolated from the production environment, regularly tested, and verified for integrity. Ransomware incidents are less damaging when restore procedures are well practiced and recovery time objectives are realistic.
Training, culture and managing insider risk Training programs must move beyond annual slide decks and simulated phishing emails. Build a security culture through role-specific education, continuous reinforcement, and transparent incident learnings.
Run frequent simulated phishing campaigns and follow up with just-in-time training for employees who click. Provide agents with simple, memorable rules for handling sensitive data, such as verification scripts for customer identity, masking rules for credit card numbers, and procedures for escalating suspicious requests.
Address insider risk through a combination of monitoring and supportive policies. Use data loss prevention tools to detect unusual exports of customer records. Design clear policies around moonlighting, secondary employment, and acceptable use, and ensure managers can spot behavioral changes that warrant review. When incidents involve employees, follow a structured and documented disciplinary and remediation process that protects the company while observing labor laws.
Incident response, tabletop exercises and breach notification readiness Every BPO should have a documented incident response plan that scales from a single compromised account to a major ransomware campaign. Plans must define roles, communication protocols, legal contacts, and steps for containment, eradication, and recovery.
Run tabletop exercises with cross-functional participation at least twice a year. Simulate scenarios such as a compromised client dataset, ransomware encrypting shared storage, or a social engineering attempt against executives. Tabletop exercises reveal gaps in contacts, unclear ownership of tasks, and missing evidence collection procedures long before an actual incident.
Breach notification is a dual obligation. Notify the National Privacy Commission as required by law, and prepare communication templates for affected clients and data subjects. Ensure legal counsel reviews public statements to align with regulatory timelines and to avoid language that could widen liability.
Demonstrating security to clients and passing audits Clients will ask for evidence, either as certifications, audit reports, or direct reviews. Prepare for three common channels of assurance: formal certifications, client-requested assessments, and operational reporting.
Certifications such as ISO 27001 or SOC 2 require time and rigor but are a durable way to demonstrate governance. If your client mix values those reports, invest in a certification roadmap. For PCI DSS environments, work with a Qualified Security Assessor for readiness.
For client-requested reviews, maintain an organized evidence repository. Document policies, training records, change-management logs, and incident response playbooks. Offer clients the ability to review controls through approved, controlled demonstrations rather than ad hoc access. Operational dashboards showing patch status, uptime, and recent incident metrics can also reassure client stakeholders.
A practical roadmap to improve BPO security Philippines now Start with a baseline assessment. Inventory data flows, systems, and third-party dependencies. Identify the crown jewels, meaning data and processes whose compromise would cause the most harm to clients or operations. From there, prioritize controls that reduce risk quickly and measurably.
Begin with hardening steps that reduce the majority of risk: enforce MFA for all administrative and remote access, patch critical vulnerabilities, segregate sensitive systems, and implement daily backups with isolated retention. Next, strengthen the human element with targeted training and improved onboarding/offboarding controls. Parallel to technical work, document policies and begin evidence collection for audits.
Measure progress with clear metrics such as time to patch critical vulnerabilities, phishing click rates, mean time to detect and respond, and percentage of systems with endpoint protection. These operational metrics matter to clients more than statements of intent.
Balancing security with operational efficiency and agent experience Security measures must fit the operational reality of high-volume contact centers. Avoid controls that create excessive friction for agents or that lengthen call times unnecessarily.
Design authentication and verification workflows that are secure and fast. Use tokenization and masking to minimize agent exposure to cardholder data. Where monitoring is required, minimize privacy concerns by redacting nonessential information and limiting recordings to the scope required by the client.
When possible, automate compliance tasks such as patch deployment, access attestations, and log retention. Automation reduces manual error and frees teams to focus on higher-value security issues.
Final thoughts BPO security Philippines demands a practical, repeatable approach that fits the scale and pace of outsourced services. Protecting client data and maintaining service continuity are not separate objectives. They are the same business requirement, expressed through policies, technology, people, and measurable processes. Start with high-impact controls such as MFA, segmentation, backups, and role-based access, then build a culture of security through training, exercises, and transparent client reporting. With a structured roadmap, Philippine BPOs can reduce risk, meet regulatory obligations, and demonstrate the reliability that global clients expect.